SBOMBox · SBOM quality and CRA readiness
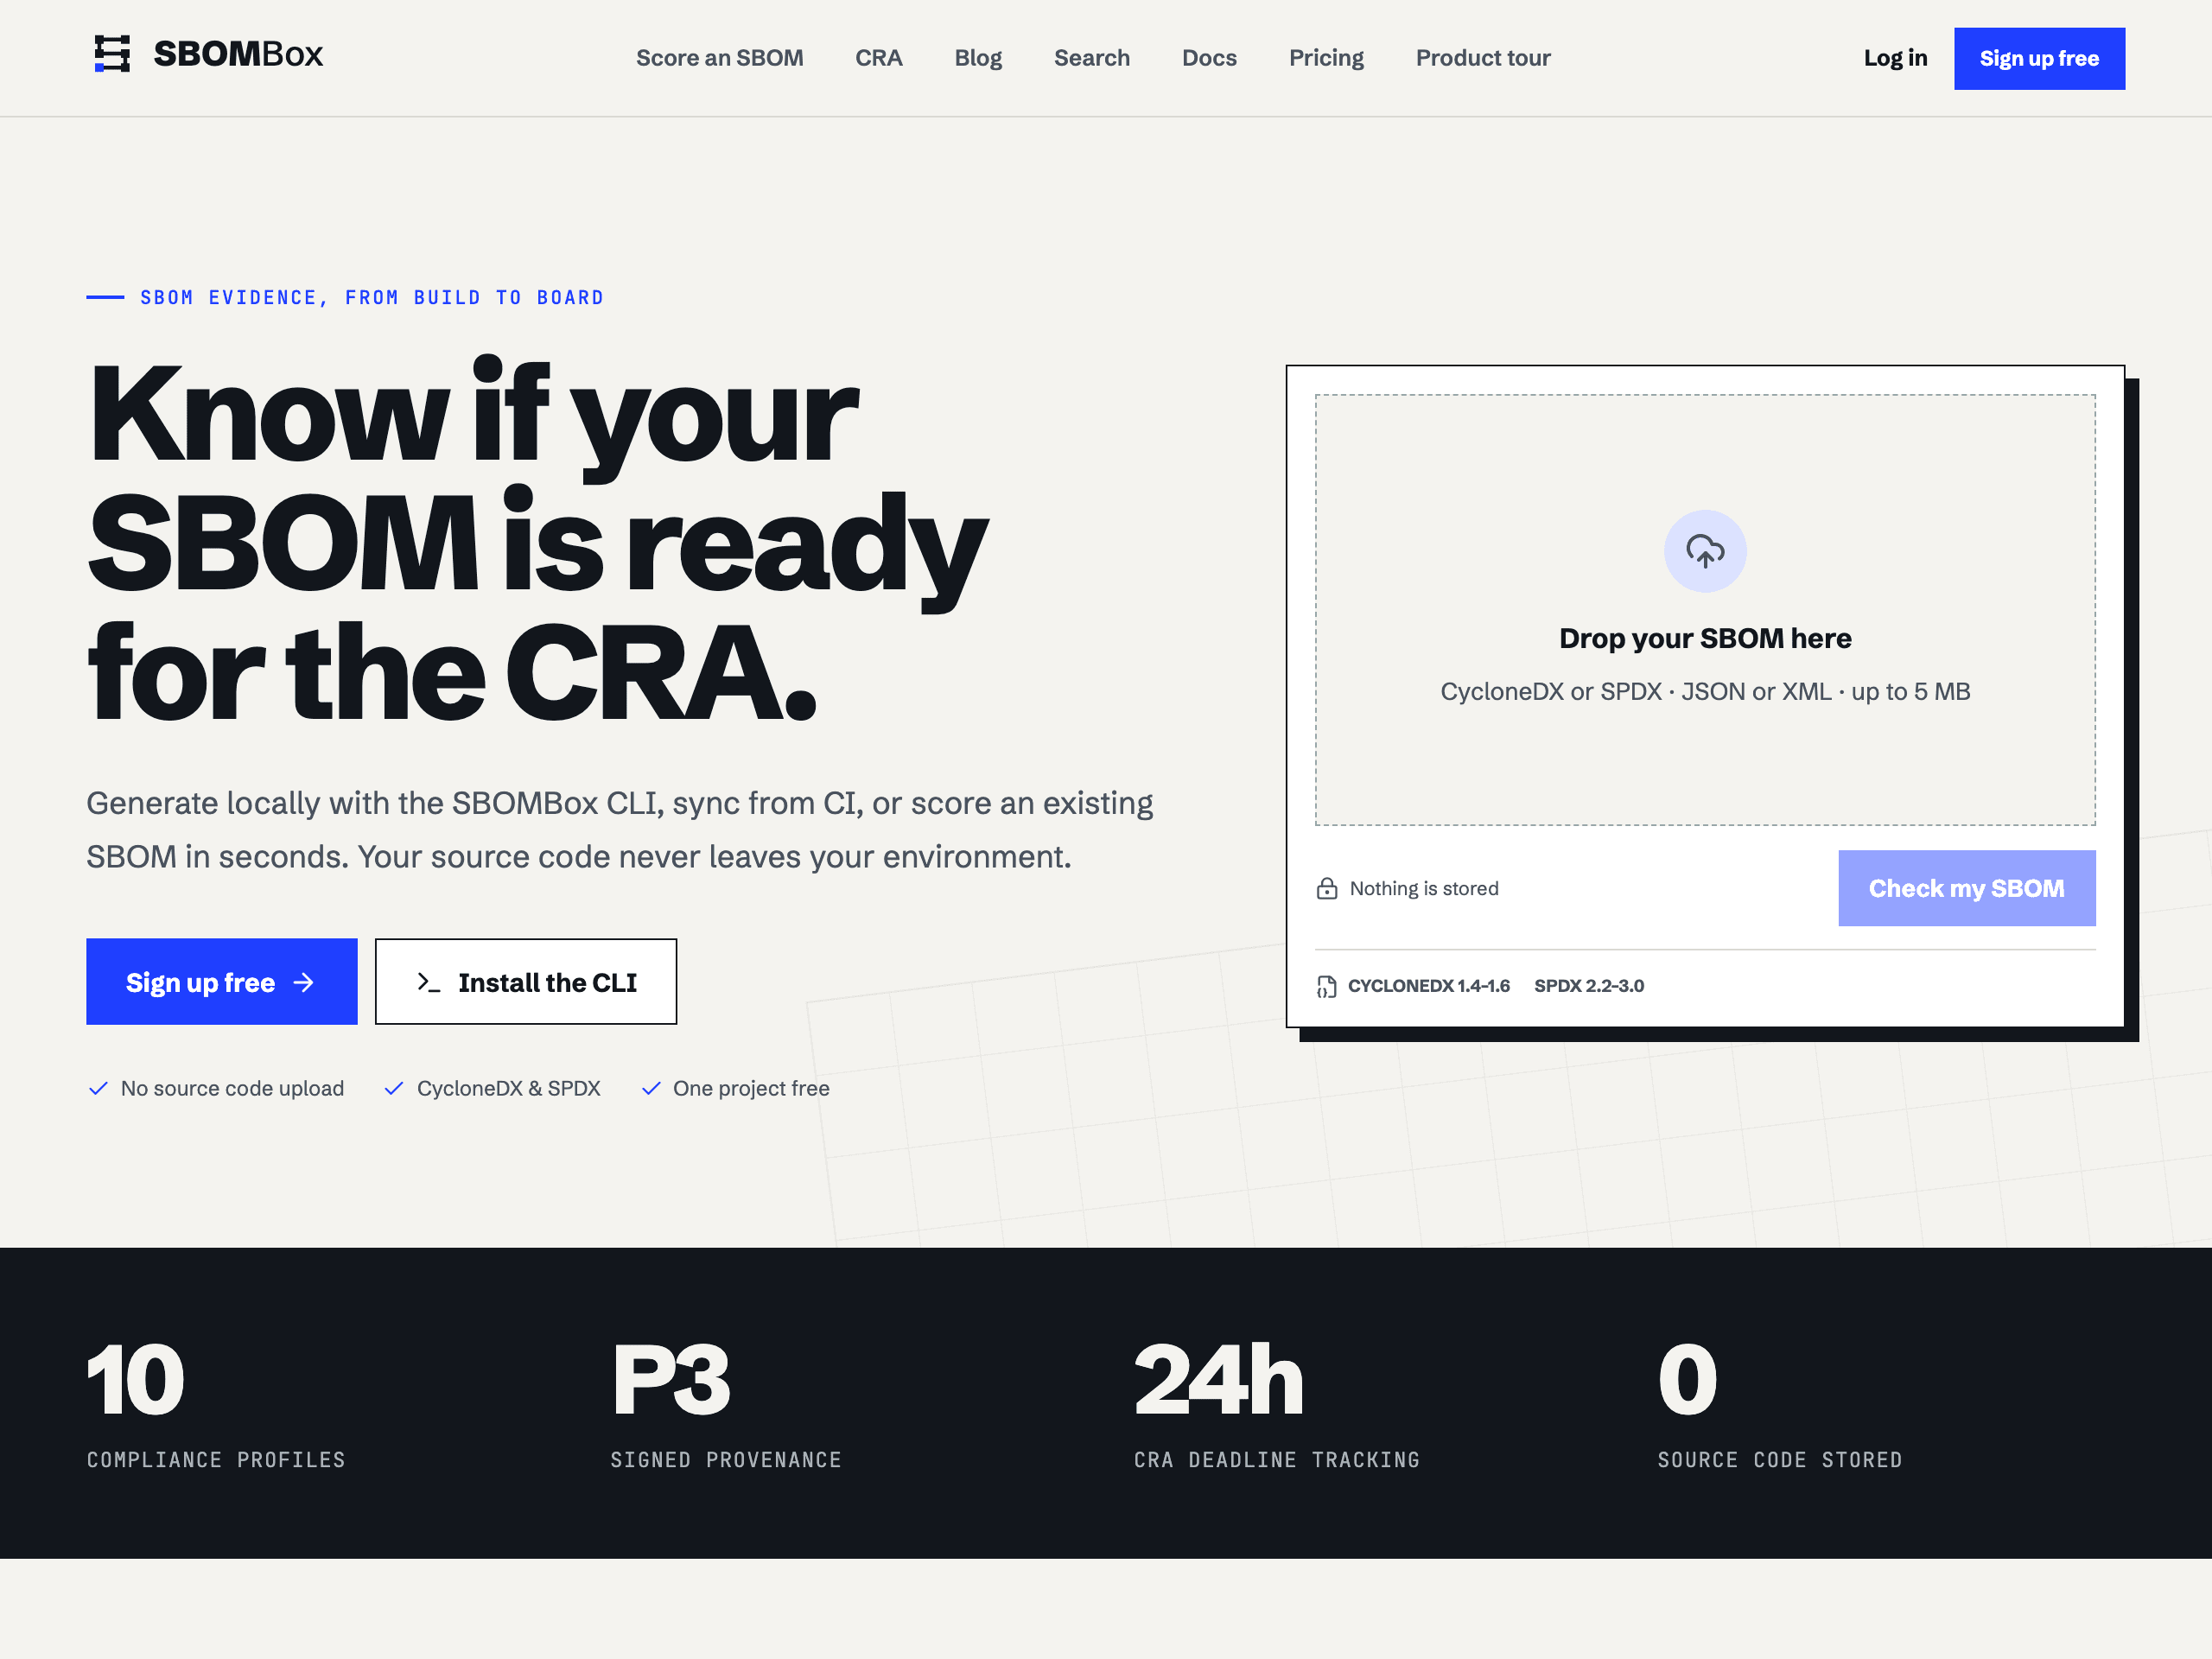
Know if your SBOM is ready for the CRA.
SBOMBox generates SBOMs where your code lives, scores them against published requirements, watches them for new vulnerabilities and keeps signed proof for every release, so you can show CRA and procurement readiness instead of guessing.
- compliance profiles across BSI, CISA, NTIA and CRA
- 10
- formats: CycloneDX 1.6 and SPDX 2.3
- 2
- lines of your source code stored
- 0
- free tier for one project
- $0
The problem
Having an SBOM is not the same as being ready.
The EU Cyber Resilience Act, US federal buyers and enterprise procurement now ask for SBOMs, vulnerability handling and proof. Most teams can generate a file. Few can show it is complete, current and trustworthy.
SBOMs are generated, then forgotten
A file in a build artifact tells nobody whether required fields are present, suppliers are named or hashes exist.
Every regulator reads them differently
BSI TR-03183-2, CISA minimum elements, NTIA and the CRA each define complete in a different way.
Vulnerabilities outrun release cycles
A newly exploited CVE can land in a shipped release, and the CRA gives you 24 hours to send an early warning.
Why we care
Readiness you can prove, not assert.
When a customer, assessor or federal buyer asks you to prove your software supply chain is under control, a bare SBOM file is not an answer. They want to know it is complete against the right standard, current against today's vulnerabilities and backed by a trail they can verify.
We built SBOMBox so that evidence is a lookup rather than a fire drill: findings name the rule and the fix, and every release keeps signed, tamper-evident proof.
How we solved it
One evidence chain from commit to audit.
SBOMBox generates SBOMs where your code lives, scores them against published requirements, watches them for new vulnerabilities and keeps signed proof for every release.
01
Generate locally, source never leaves
The CLI and CI action build CycloneDX or SPDX SBOMs inside your environment and upload only the resulting metadata, with OIDC-attested runs and no long-lived secrets.
02
Audit against published profiles
Every field is checked against BSI, CISA, NTIA and CRA profiles. Each finding names the rule, the affected components and the fix, with score history per release.
03
Monitor for new vulnerabilities
Daily matching against vulnerability feeds with KEV and EPSS context, plus CRA 24h and 72h reporting clocks that start the moment you triage, and VEX decisions kept with the release.
04
Prove it to auditors
P3 signed provenance, a hash-chained audit log with verification, and shareable public report links let customers and assessors verify instead of trust.
How it works
Three steps, no setup.
01
Generate an SBOM
Use the CLI or a CI action, or drop in an existing CycloneDX or SPDX file to score in seconds.
02
Get requirement-level results
See a quality score plus every finding mapped to the rule it fails and the fix.
03
Monitor and share proof
Watch releases for new vulnerabilities and hand auditors a signed, verifiable report.
Privacy
Generated locally. Source never leaves.
The CLI and CI action build SBOMs inside your own environment and upload only the resulting metadata. Your source code is never stored.
How we handle data →- Zero source code stored: only SBOM metadata is uploaded
- OIDC-attested CI runs, so there are no long-lived secrets to leak
- Signed provenance and a hash-chained audit log you can verify
Who it is for
Built for teams that cannot afford to guess.
Security and compliance teams
Answer CRA, procurement and customer security questions with a verifiable trail.
Engineering and DevOps
Generate SBOMs in CI with OIDC-attested runs and no long-lived secrets to manage.
Vendors to public-sector buyers
Meet SBOM and vulnerability-handling expectations without rebuilding evidence by hand.
Teams selling to enterprises
Turn supply chain readiness into a shareable trust center instead of a sales blocker.
SBOMBox questions
Which SBOM formats does SBOMBox support?
CycloneDX 1.6 and SPDX 2.3, generated with the CLI or CI action, or uploaded to score an SBOM you already have.
Does it store our source code?
No. Generation happens inside your environment and only the resulting SBOM metadata is uploaded. Your source code is never stored.
Is an SBOMBox report a certification?
No. It checks your SBOM against published rules from BSI, CISA, NTIA and the CRA. It is evidence of readiness, not legal advice or a certification.
Need more than the product?
We build it into your workflow.
SBOMBox is one example of what we engineer. If you need it connected to your systems, or running inside your own infrastructure, our team designs, builds and operates it for you.
How an engagement works →